
Phishing Simulation Programs: Improving Employee Cyber Awareness
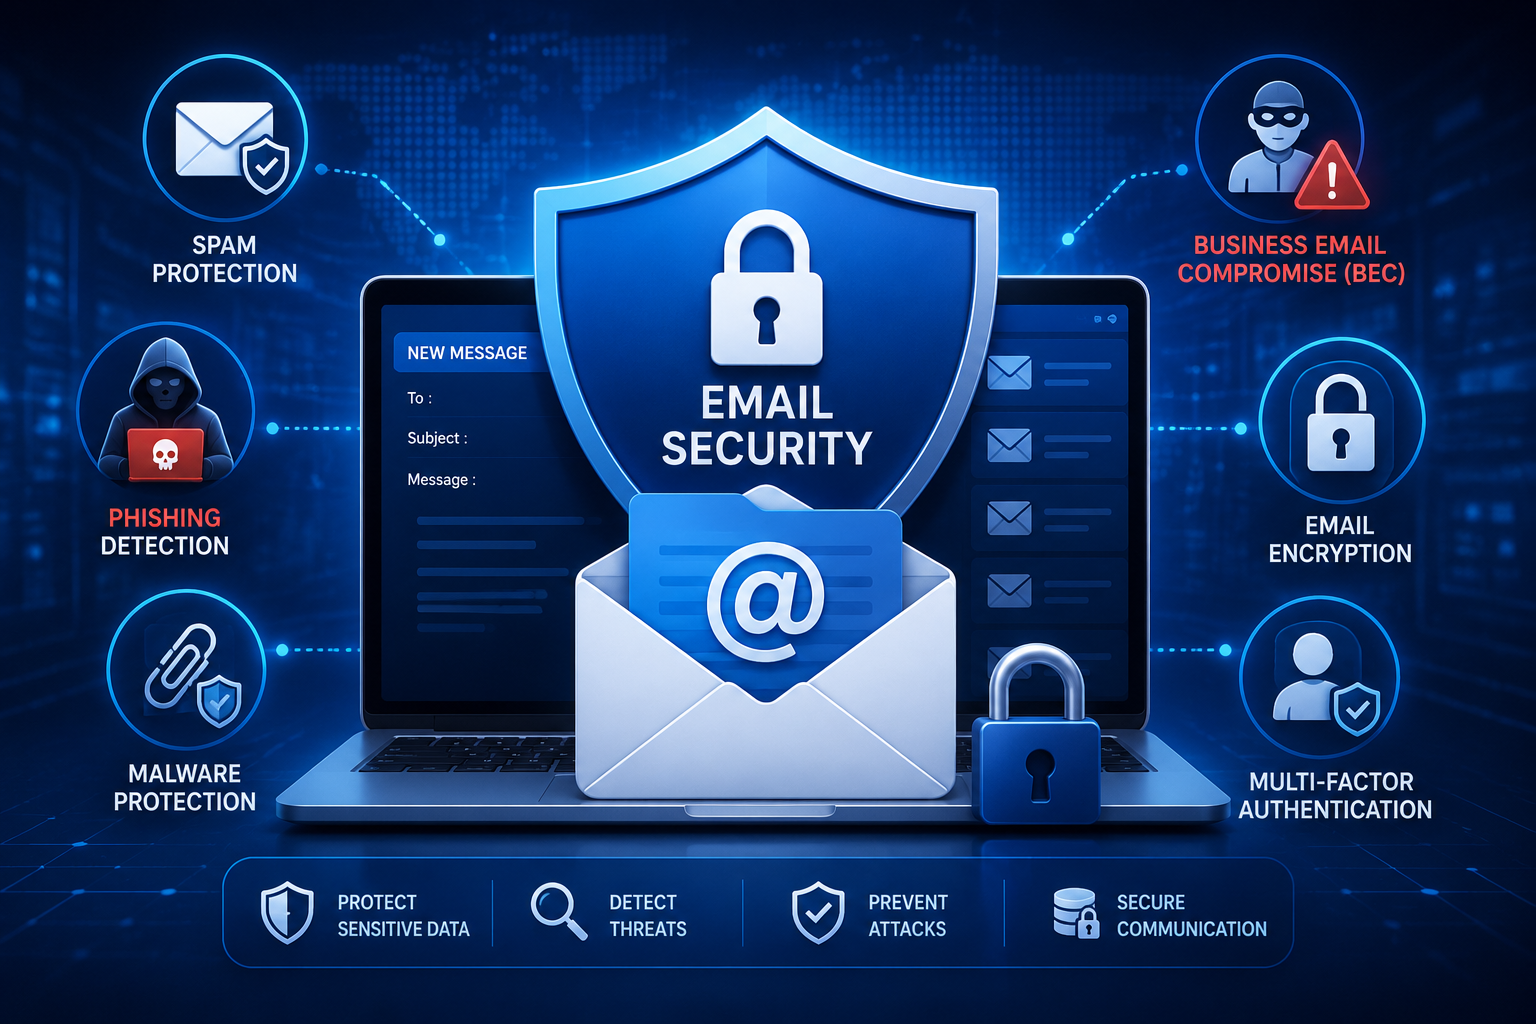
IntroductionCybersecurity threats do not always begin with advanced technical attacks. Many incidents start with a simple email that tricks an employee into clicking a suspicious link, downloading an attachment, or sharing confidential information. Phishing remains a common method used by attackers to target people and gain unauthorized access to business systems.Phishing simulation programs help organizations prepare employees to recognize these threats through controlled, educational exercises. By combining realistic simulations with practical training, businesses can improve cyber awareness and encourage safer online behavior.What Are Phishing Simulation Programs?A phishing simulation program is a security awareness activity in which an organization sends controlled, simulated phishing messages to employees. These messages imitate common attack techniques without exposing employees to real malicious content.The purpose is to understand how employees respond to suspicious emails and identify areas where additional training may be needed. The results can help security teams develop more effective awareness programs.Why Phishing Simulations Are Important1. Identify Human-Related Security RisksEmployees may respond differently to urgent requests, unexpected attachments, password-reset notifications, or messages that appear to come from trusted sources. Simulations help organizations understand these response patterns and identify where employees need support.2. Improve Email Threat RecognitionTraining helps employees recognize warning signs such as unfamiliar senders, unusual links, unexpected requests for sensitive information, and suspicious attachments. Repeated learning opportunities can help employees approach unexpected messages more carefully.3. Encourage Safer Workplace HabitsEmployees who understand common phishing techniques may become more cautious before clicking links or sharing information. A strong awareness program encourages people to verify suspicious requests and follow established security procedures.4. Support Security Awareness PlanningSimulation results can help organizations identify common mistakes and plan targeted training. Instead of providing identical guidance to everyone, security teams can focus on the topics and behaviors that need the most attention.How to Build an Effective Phishing Simulation ProgramStep 1: Define Clear ObjectivesStart by deciding what the organization wants to improve. Objectives might include reducing clicks on suspicious links, increasing reporting of suspected phishing emails, or improving awareness of credential theft attempts.Clear objectives make it easier to measure progress over time.Step 2: Select Relevant Simulation ScenariosChoose scenarios that reflect the types of messages employees may encounter, such as fake delivery notifications, password-reset requests, invoice messages, or impersonation attempts.Simulations should remain controlled and appropriate for the workplace. They should support learning rather than create unnecessary fear or embarrassment.Step 3: Conduct the SimulationRun the exercise using an approved security awareness platform or an authorized internal process. Ensure that the activity follows organizational policies and applicable privacy requirements.Employees should not be exposed to actual malware or real credential collection during the exercise.Step 4: Provide Immediate Educational FeedbackWhen an employee interacts with a simulated phishing message, provide clear guidance explaining the warning signs and the safer action to take. This turns the exercise into a learning opportunity rather than simply recording a mistake.Step 5: Offer Targeted TrainingUse the results to identify subjects that require additional explanation. For example, employees who struggle to identify suspicious links may benefit from practical demonstrations, while others may need guidance on verifying requests from senior staff.Step 6: Repeat and EvaluateConduct simulations periodically and compare results across similar exercises. Use the findings to improve training materials, communication, and reporting procedures.Key Metrics to Measure SuccessOrganizations can monitor several indicators to evaluate their phishing awareness efforts:Click rate: The percentage of recipients who click a simulated phishing link.Submission rate: The percentage of recipients who submit information in a controlled simulation, where this action is safely simulated.Reporting rate: The percentage of recipients who report the simulated message through the approved reporting process.Training completion: The proportion of employees who complete assigned awareness activities.Repeat behavior: Whether employees show improved responses across comparable simulations over time.These metrics should be interpreted together. A lower click rate is useful, but an increase in timely reporting can also demonstrate that employees are becoming more active participants in organizational security.Best Practices for Employee Cyber AwarenessKeep Training PracticalUse examples that employees can understand and relate to their daily responsibilities. Explain how to inspect sender addresses, preview links safely, verify unusual requests, and report suspicious messages.Build a Positive Security CultureAvoid publicly naming or shaming employees who interact with simulations. A supportive environment makes it easier for employees to ask questions and report mistakes without fear.Encourage ReportingProvide a simple and clearly communicated way for employees to report suspicious emails. Security teams should acknowledge reports and explain what employees should do if they encounter a genuine threat.Include All Relevant TeamsPhishing awareness should not be limited to technical staff. Finance, human resources, customer support, management, and other departments may face different types of social engineering attempts.How Professional Cybersecurity Education HelpsPhishing simulations are most effective when supported by a wider security awareness strategy. Organizations should combine practical exercises with employee education, clear reporting procedures, and regular reviews of security risks.For more information about education-focused cybersecurity support and security awareness, visit https://www.rashicore.com/education.php.A structured approach to security education and awareness can help organizations build safer workplace habits and improve employee understanding of common cyber threats.Frequently Asked Questions1. How often should phishing simulations be conducted?The frequency depends on the organization's size, risk profile, and training objectives. Regular exercises with varied scenarios can help maintain awareness without overwhelming employees.2. Are phishing simulations safe?They can be conducted safely when properly authorized and designed for education. Simulations should avoid real malware, actual credential collection, and unnecessary exposure of employee information.3. What should happen when an employee clicks a simulated phishing link?The employee should receive clear, timely feedback explaining the warning signs and the appropriate response. The goal is to improve understanding, not to punish employees for making a mistake.4. How can organizations measure improvement?Organizations can compare click rates, reporting rates, training completion, and repeat behavior across comparable exercises. Results should be reviewed alongside other security awareness indicators.ConclusionPhishing simulation programs help organizations understand employee responses to common cyber threats and identify opportunities for better security education. When combined with practical training, supportive feedback, and clear reporting procedures, these programs can strengthen awareness and encourage safer workplace behavior.Building cyber awareness is an ongoing process. Regular simulations and continuous learning help employees recognize suspicious messages, respond appropriately, and contribute to a stronger security culture.Visit Website: https://www.rashicore.com/education.php
Read More →












 UK
 USA
 UAE
 Canada
 Australia
 Germany
 Singapore
 Netherlands